

[ad_1]
Key Takeaways:
“GitVenom” exploits pretend GitHub repositories embedded with malware to focus on cryptocurrency customers.Cyber attackers are leveraging AI-driven deception ways to trick customers into downloading malicious software program disguised as reliable open-source initiatives.Mitigating these rising threats requires thorough code opinions and safe growth practices.
Open-source software program growth — a bedrock of innovation and collaboration — is more and more below siege. Drawing from the work of Kaspersky’s Clemens Lutz and colleagues, GitVenom is a extremely subtle marketing campaign that exploits the inherent belief in free platforms to distribute malware and compromise customers. Because the disastrous fallout of this complicated assault demonstrates, it’s more and more very important that members of the general public have a pointy and proactive method to on-line safety. The severity of those threats is obvious within the case of a developer who misplaced 5 Bitcoin (price roughly $442,000 on the time) in a single devastating assault.
Mimicking an Artist: Analyzing the GitVenom Methodology
Kaspersky has performed an in-depth evaluation of the GitVenom marketing campaign, led by analyst Georgy Kucherin. Hackers leveraged GitHub’s ‘Discover’ function to extend the visibility of their pretend initiatives, which contained malicious code designed to contaminate customers’ programs. These aren’t simply amateurish makes an attempt: the attackers present a transparent understanding of the open supply ecosystem, and are utilizing ever extra subtle strategies to trick their targets.
Usually, these made-up initiatives appear pragmatic and enticing, addressing widespread developer wants and pursuits:
Bitcoin Pockets Administration Telegram bots: These fraudulent bots exploit the recognition of crypto buying and selling automation, promising comfort whereas delivering malware. They provide seamless pockets administration, however ship a nasty payload.Instagram Automation Instruments: Marketed to social media lovers and entrepreneurs, they pack thrilling automation options with hidden system infections.Sport hacking instruments: These lure players with the promise of enhancing their efficiency in widespread titles like Valorant, however as a substitute set up adware.
A defining trait of the GitVenom marketing campaign is the trouble invested in making these initiatives seem genuine. Attackers are making the most of synthetic intelligence (AI) to create complete and arguably skilled paperwork. These AI-generated README information present multilingual directions and explanations, including a veneer of legitimacy to the in any other case nefarious instruments. The superior strategies utilized by GitVenom attackers make it even more durable for seasoned builders to tell apart between reliable and fraudulent initiatives.
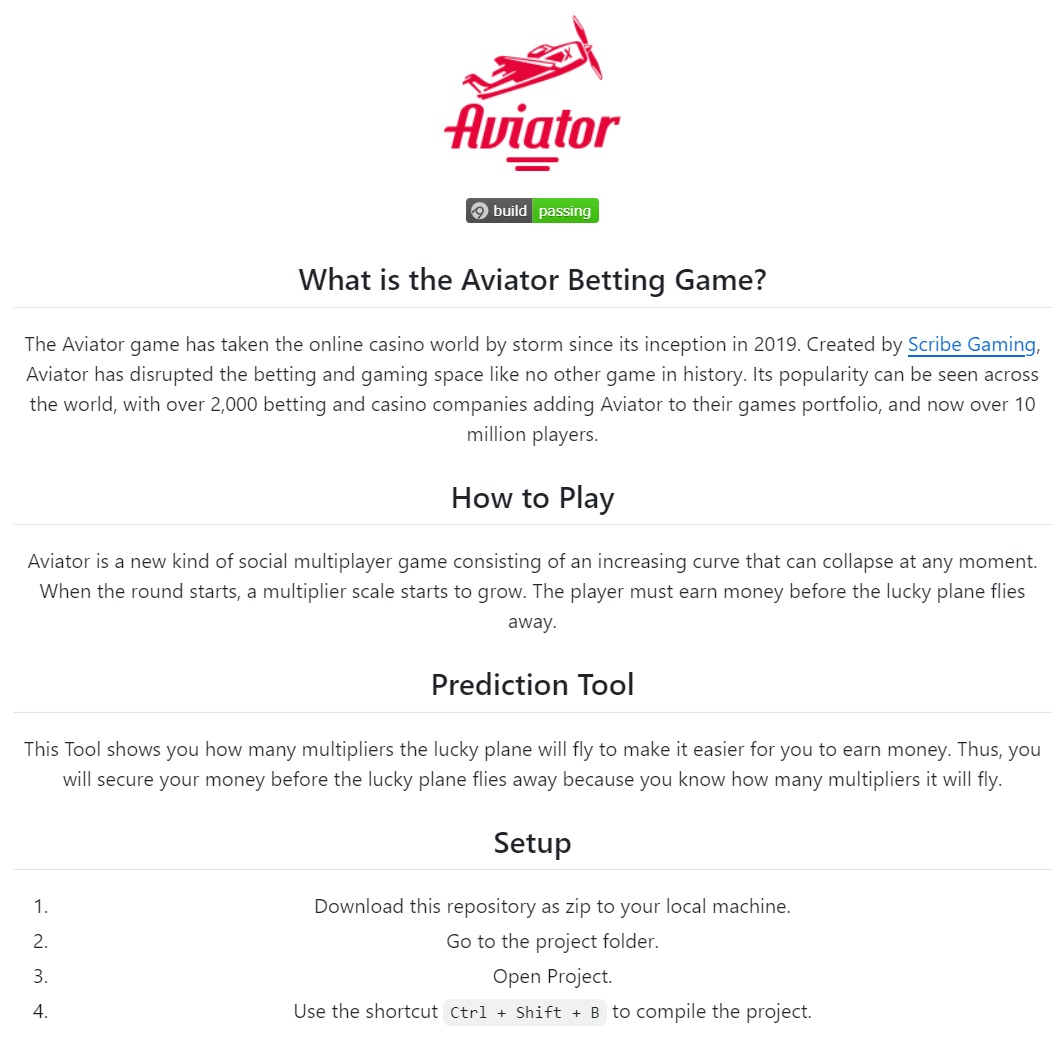
Instance of a ‘well-designed’ instruction file, as referred to by Kaspersky
As Kucherin identified convincingly, the writing is on the wall — the creators of the offending marketing campaign have “gone to nice lengths to make the repositories seem reliable to potential targets,” an train in figuring out human psychology and trust-building, albeit one that’s essentially superficial.
Subjecting the Phantasm to Itself: The Double Bind of the Synthetic Inflation of Exercise
Along with the AI-generated documentation, the GitVenom attackers make the most of numerous different manipulative ways to bolster the façade of legitimacy. A key tactic is artificially inflating the variety of “commits” – data of code adjustments made to a mission – to create a false sense of exercise. The attackers preserve a relentless stream of seemingly energetic commits to the mission by repeatedly touching timestamp information with the present date, making it seem that the mission continues to be actively maintained and developed.
Manipulating exercise logs is a key a part of GitVenom’s success, because it exploits the assumption that actively maintained initiatives are safer. However this buzz of exercise seems to be nothing however a smokescreen with malicious functions mendacity behind it, because it’s not a whole program.
The Malicious Arsenal: Understanding the Threats Hidden Inside
The precise GitVenom initiatives have deceptive entrance ends that result in a number of varieties of malware that may assist compromise programs or steal precious property from customers. These payloads usually comprise a mixture of:
Information Stealers: Malicious applications that intention to extract delicate info from compromised programs, together with usernames, passwords, cryptocurrency wallets, searching historical past, and any sort of private knowledge. The pilfered information are subsequently compressed and despatched to the attackers by way of encrypted communication channels like Telegram.Clipboard Hijackers: These sneaky purposes watch the system clipboard for cryptocurrency pockets addresses. When a sufferer copies a pockets deal with (to make a transaction), the clipboard hijacker quietly replaces it with the deal with to the attacker’s pockets.Distant Entry Trojans (RATs): RATs present attackers with full system management by permitting them to observe consumer exercise, seize screenshots, log keystrokes, execute instructions and take management of your machine solely. Such “excessive” entry permits attackers to exfiltrate delicate info, drop further malware or use the contaminated system as half of a botnet.
By implementing such proactive steps, builders can considerably scale back the danger of being affected by the GitVenom marketing campaign and different related cyber threats.
Extra Information: Bybit Suffers Huge $1.4 Billion Hack: What You Have to Know
GitVenom: A International Menace, Unfold Throughout Geographies
Kaspersky’s analysis has indicated particular areas of the world experiencing increased prevalence of the menace, regardless of the GitVenom marketing campaign being witnessed in a number of areas globally. GitVenom infections have been reported in areas equivalent to Russia, Brazil, and Turkey, indicating the next prevalence in these areas. The geopolitical impression of GitVenom has obtained restricted but vital media consideration, particularly in areas the place open-source growth is widespread.
The Darkish Aspect of GitHub — A Double-Edged Sword Of Software program Growth
Serving as the biggest collaborative software program growth surroundings, GitHub has change into an indispensable software for builders worldwide. However after all, its open nature additionally makes it a goal for dangerous actors. And the identical options that make GitHub so precious — its large storehouse of open-source code, its collaborative dev instruments, and its giant neighborhood — may also be abused by attackers trying to distribute malware and exfiltrate delicate info.
As GitHub has grown in reputation, and due to the belief that’s given to open-source code, it supplies a singular alternative for attackers to hit an enormous variety of potential victims with a single marketing campaign that has been well-tailored. As Kucherin notes, “Code-sharing platforms equivalent to GitHub are utilized by hundreds of thousands of builders worldwide, [so] menace actors will proceed utilizing pretend software program as an an infection lure.”
Constructing Your Protection: Methods to Defend Your self on GitHub
With the subtle nature of the GitVenom marketing campaign and the dangers concerned in leveraging open-source code, builders could be clever to take a proactive and multi-layered method to safety. Kaspersky recommends the subsequent steps:
Code Evaluation: One other helpful apply is to research any third-party code earlier than integrating it into your initiatives to establish suspicious patterns or hidden malware.Use Robust Malware Safety: Ensure that your computer systems and cell units use antivirus software program and different safety instruments which might be updated.Verify Undertaking Indicators Fastidiously: Be cautious of initiatives with newly created accounts, few stars, and up to date creation dates.Obtain Recordsdata with Warning: Don’t obtain information by way of direct hyperlinks shared inside chats, unknown channels and unverified web sites. If the file features a hyperlink to the GitHub repository, you must at all times go there to obtain the file as a substitute.Monitoring GitHub for Malware: Attackers incessantly abuse GitHub’s open nature to distribute their malicious software program.Verify for Undertaking Authenticity: Earlier than executing any downloaded code, make it possible for the mission is genuine and ensures there are not any detrimental opinions from different builders. Be cautious of READMEs which might be overly polished or commit histories which might be too uniform.
In conclusion, taking these preventive actions will assist builders to mitigate their possibilities of getting contaminated by the GitVenom marketing campaign or any such future campaigns.
No Mounted Sample — Fixed Vigilance Required
Maintaining with rising cyber threats and evolving assault ways is crucial to staying protected. Kaspersky mentioned it expects attackers to maintain releasing malicious initiatives, “probably with small adjustments” of their ways, strategies and procedures (TTPs). This confirms a requirement for alert and a dedication to find novel threats and safety greatest practices.
The battle in opposition to cybercrime is ongoing, and GitVenom is only one of many evolving threats concentrating on builders and cryptocurrency customers. Keep vigilant and proactive to attenuate dangers and shield your self and others on-line.
[ad_2]
Source link


